
Application Management
Unrecognized NameID - user won't be autoprovisioned: No SAML groups received
This document provides steps to resolve one of the common error messages encountered during the configuration or use of SSO with the Identity Service Provider.
First published date
10/15/2021 1:09 PM
Last published date
10/15/2021 1:09 PM
Overview
Unrecognized NameID error occurs when there is missing or incorrect information entered during the SAML setup. You can resolve these issues through an identity provider (IDP) of your choice.
Product section
Loggly
Cause
1. No configured or misconfigured the user attribute to the IDP
example: groups or Groups
2. If the user specified in the group names in the Role Mapping Section is not mapped correctly.
example: groups or Groups
2. If the user specified in the group names in the Role Mapping Section is not mapped correctly.
Resolution
1. The user attributes should be present and configured to their desired attributes. It's either groups or Groups.
2. The group names setup in the Role Mapping Section is existing in your IDP and the email address should be mapped to the group name according to desired roles/permission.
This is an example for Okta IDP: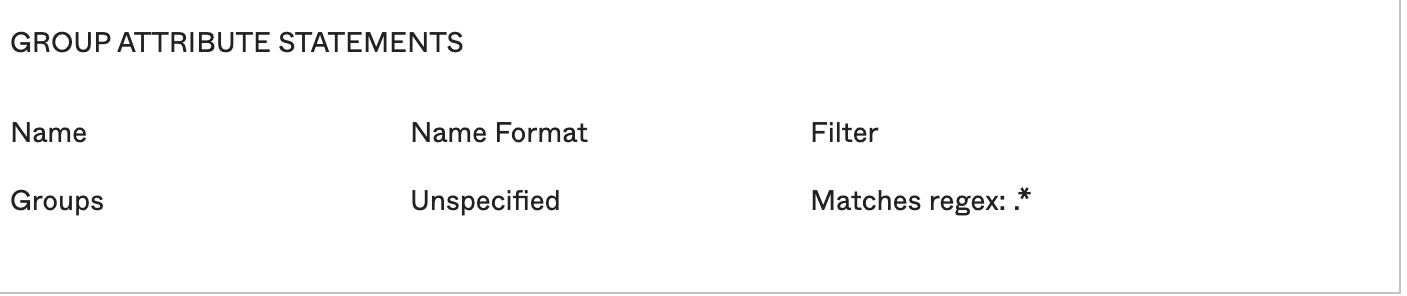
2. The group names setup in the Role Mapping Section is existing in your IDP and the email address should be mapped to the group name according to desired roles/permission.
This is an example for Okta IDP: