
Security Compliance
Integrate Forcepoint log collection in SEM
This article provides steps on how to configure log monitoring for logs received from Forcepoint Next Generation Firewall device
First published date
9/23/2020 10:10 AM
Last published date
9/23/2020 10:10 AM
Overview
So, you have SEM and you have Forcepoint Next Generation Firewall Device and like to forward and monitor their logs in SEM.
You have come to the right place, follow the steps in resolution steps below.
You have come to the right place, follow the steps in resolution steps below.
Product section
Security Event Manager
Cause
na
Resolution
Part 1: Enable and Configure Log Forwarding on Forcepoint SMC2 GUI console
1. Login to your Forcepoint SMC2 Web GUI
2. Click on Others tab on left
3. Click on Log Server a popup window opens which allows to configure log forwarding.
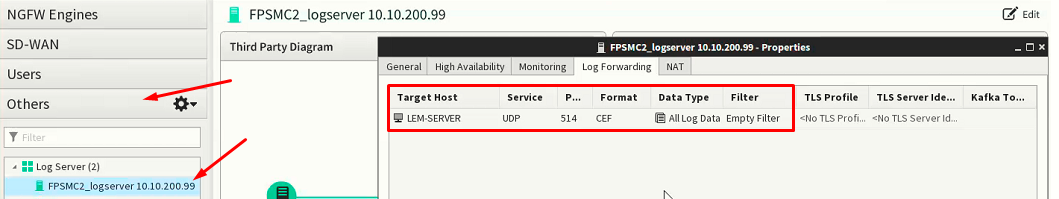
4. Click on Lof Forwarding Tab and fill in the Syslog forwarding info like IP, Service, Port, Format and DataType and make sure to select log CEF format here(SEM only supports this format as of now). Example:
Refer to vendors official page on Configure Forcepoint log forwarding for rest of the steps.
5. Click okay and save the config changes.
Part 2: Configure the Forcepoint Connector
Refer to How to Configure a Syslog Connector on SEM and choose the McAfee ForcePoint Firewall
Make sure to set the log file path in connector to either Syslog.log/Kern.log after verifying if this where logs are received via cmc>appliance>checklogs first to find where the logs are received.
(Screenshots property of © 2022 Forcepoint LLC)
1. Login to your Forcepoint SMC2 Web GUI
2. Click on Others tab on left
3. Click on Log Server a popup window opens which allows to configure log forwarding.
4. Click on Lof Forwarding Tab and fill in the Syslog forwarding info like IP, Service, Port, Format and DataType and make sure to select log CEF format here(SEM only supports this format as of now). Example:
Refer to vendors official page on Configure Forcepoint log forwarding for rest of the steps.
5. Click okay and save the config changes.
Part 2: Configure the Forcepoint Connector
Refer to How to Configure a Syslog Connector on SEM and choose the McAfee ForcePoint Firewall
Make sure to set the log file path in connector to either Syslog.log/Kern.log after verifying if this where logs are received via cmc>appliance>checklogs first to find where the logs are received.
(Screenshots property of © 2022 Forcepoint LLC)